


[ KEY FEATURES ]
Ensure Your Code is
Secure, Efficient, and Compliant
Protect and strengthen your code by leveraging AuditAgent, our AI smart contract security tool.
01
Automated Vulnerability Detection
Scans your code for vulnerabilities and potential threats, identifying issues before they become critical. With deep analysis and smart contract scanning, you can deploy faster without compromising security.

02
AI-Powered Insights
Creates summaries and diagrams of your codebase, and generates invariants you can reuse in your test suite.

03
Persistent Memory
Your next scan already knows the project. AuditAgent carries approved architecture, invariants, hypotheses, contradictions, custom instructions, and excluded findings into future scans. You decide what becomes long-term memory.

04
MCP Integration
Run AuditAgent from Claude Code, Cursor, or another MCP client. Upload code and start a scan from your coding agent; AuditAgent emails you when the report is ready. MCP documentation
[ HOW IT WORKS ]

1
Connect Your Repository
Integrate with GitHub or any other code repository. We automatically start scanning your smart contracts.

2
Full Security Analysis
Our AI-driven tool leverages static and dynamic analysis to detect hidden vulnerabilities and optimizations.

3
Review Your Report
Receive a comprehensive report with detailed findings and actionable recommendations.
[ WHY CHOOSE AUDITAGENT? ]
Build Confidently
Save Time, Resources, and Effort
Cut weeks of security overhead with our AI smart contract audit tool, rapidly detecting critical risks so you can focus on building your product.
Enhanced Security and Protection
Our AI code analysis simulates attacks across multiple vectors, offering deeper insights than regular tools, while proactively detecting vulnerabilities others miss.
Comprehensive Reporting
Receive detailed vulnerability reports with complete descriptions, insights, and code snippets. Our analytics simplify security, making it easy to resolve issues.
[ SUPPORTED ECOSYSTEMS ]
Scan Solidity, Cairo and Rust Smart Contracts
Solidity — EVM
Scan Solidity contracts across Ethereum and EVM-compatible chains. Scan a repository, or point AuditAgent at an already-deployed contract on-chain.
Reads .sol sources.
Cairo — Starknet
Scan Cairo contracts for Starknet. Same pipeline, same pricing, same scan limits as EVM — from the team that builds Starknet infrastructure.
Reads .cairo sources.
Rust — Solana
Scan Solana programs written in Rust. Point AuditAgent at your repository and it applies Solana conventions when reading the code.
Reads .rs sources.
[ PRICING ]
Our Dynamic Pricing
Choose the depth that fits your workflow.
[ TESTIMONIALS ]
Trusted by Industry Leaders
With Nethermind's AI-supported analysis, we're raising the assurance bar for tokenized securities and CMTAT, which is the most robust and versatile standard in the space. Thanks to Nethermind for the depth of the work and to UBS for supporting a model where innovation and security move together.

Jean-Philippe Aumasson
Chair of CMTA's Tech Committee · co-Founder and CSO at Taurus SA


[ FAQ ]
Frequently Asked Questions
Most scans complete within an hour. The exact time depends on the size and complexity of your smart contract. Simple contracts may finish in under 15 minutes for a Developer scan, while larger codebases with an Auditor scan could take up to a few hours.
AuditAgent is trained on an extensive database of real-world smart contract audits. This allows it to understand context and intent, significantly reducing false positives compared to traditional static analysis tools.
No. AuditAgent is designed to be accessible to all Solidity developers. Findings are presented with clear explanations and remediation suggestions, so you can act on them without deep security expertise.
Yes. AuditAgent offers API access and CI/CD integrations so you can automate security scans as part of your development workflow.
AuditAgent complements traditional audits by catching issues early in development. It helps you ship cleaner code to auditors, reducing audit time and cost — but a manual audit is still recommended for production deployments.
BLoC is AuditAgent’s pricing unit calculated as estimated BLoC equals the ceiling of tokens divided by 10. It uses token-based counting that is formatting-independent and prevents gaming. A contract with 5,000 tokens equals 500 BLoC. See the AuditAgent documentation for further details.
AuditAgent supports Solidity on Ethereum and EVM-compatible chains, Cairo on Starknet, and Rust on Solana. Pricing, scan limits, and the analysis pipeline are the same regardless of which ecosystem you scan.
[ BLOG ]
From Our Blog

April 22, 2026
Speed, Cost, and Ecosystem Coverage: The Next Constraints in AI Security Analysis

April 16, 2026
Recall Is Not Enough: False Positives and the Limits of Benchmarking
April 7, 2026
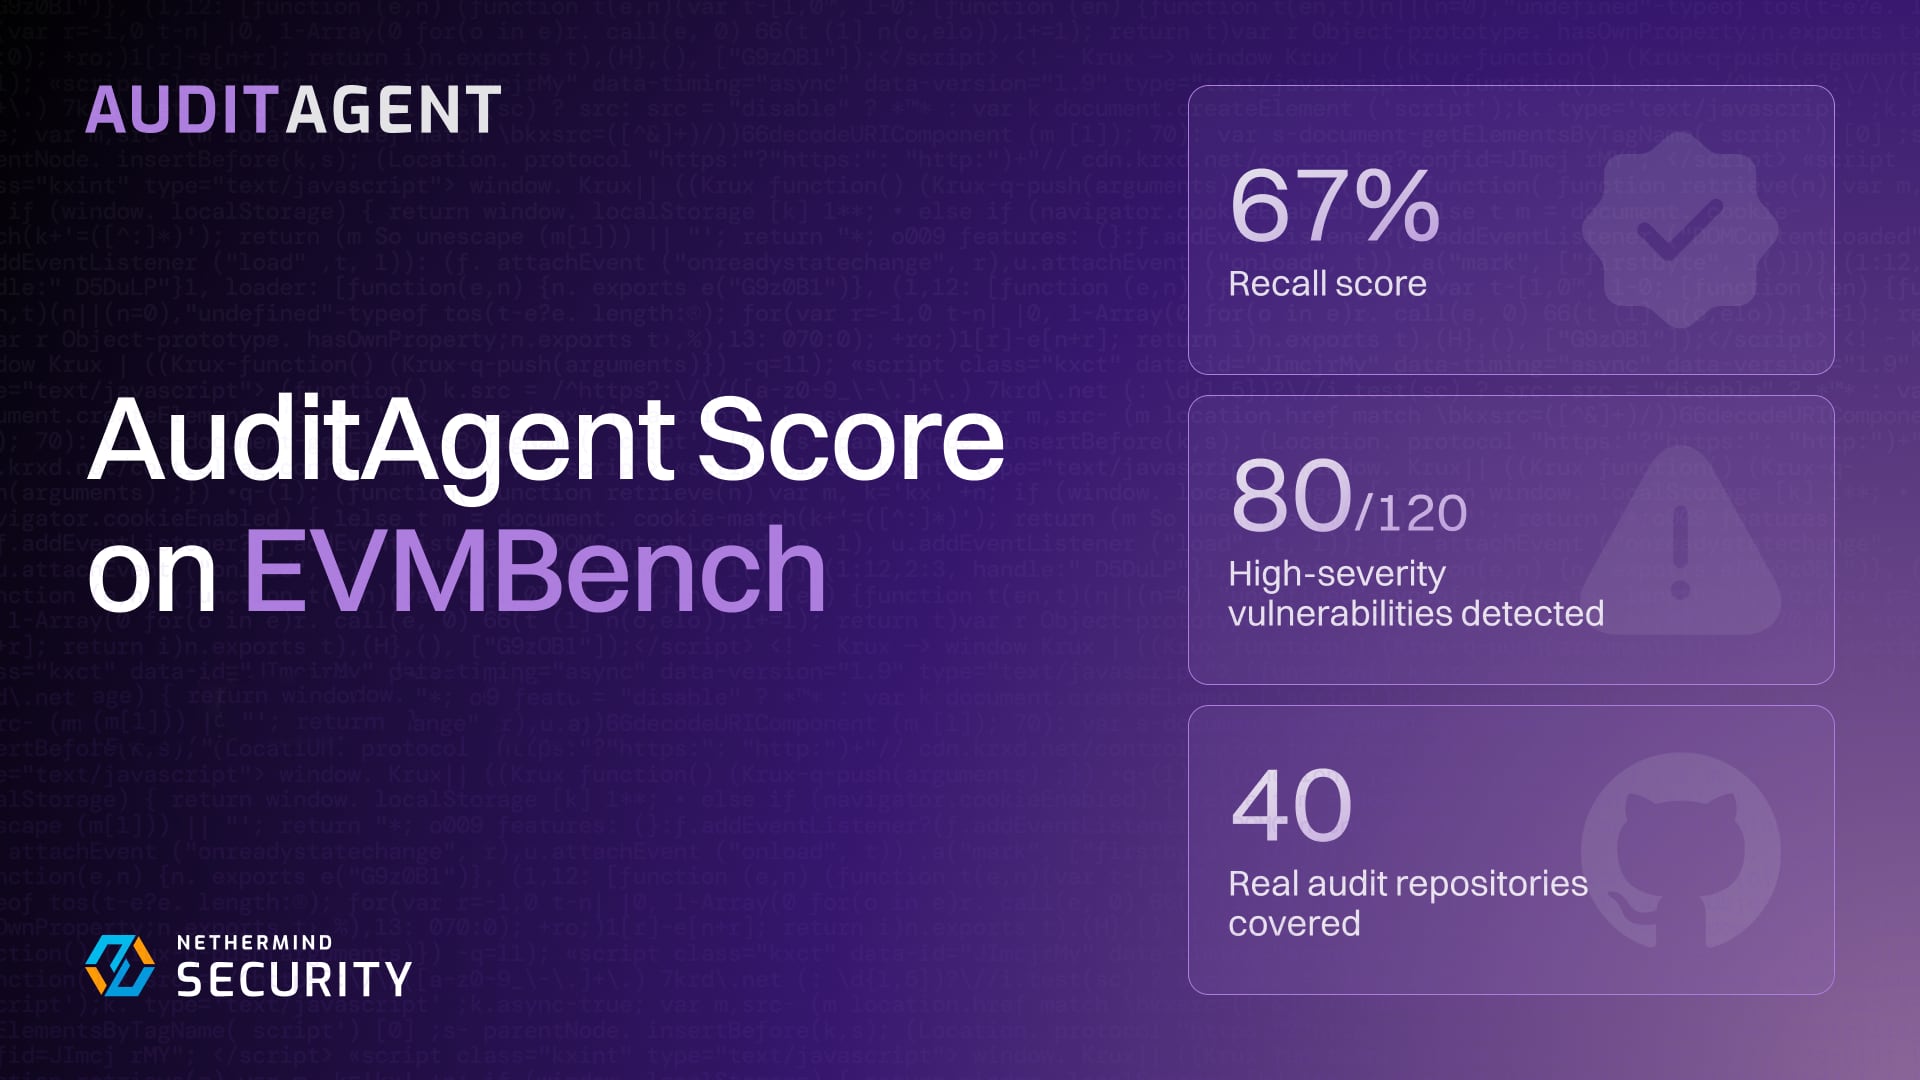
AuditAgent on EVMBench: 40 Repositories, 120 Vulnerabilities, No Repos Skipped

January 27, 2026
Using AI-assisted security analysis on the CMTAT: Case study of how CMTA and UBS have used Nethermind's AuditAgent on CMTAT contracts
[ COMPREHENSIVE AUDITS ]
While our AI tool provides automated analysis, we also offer comprehensive audits by blockchain security experts from Nethermind.
Lines of Code Audited
Vulnerabilities Found
Remedies Implemented